
Development Notes
Two pairs of public and private key functions (API mode)
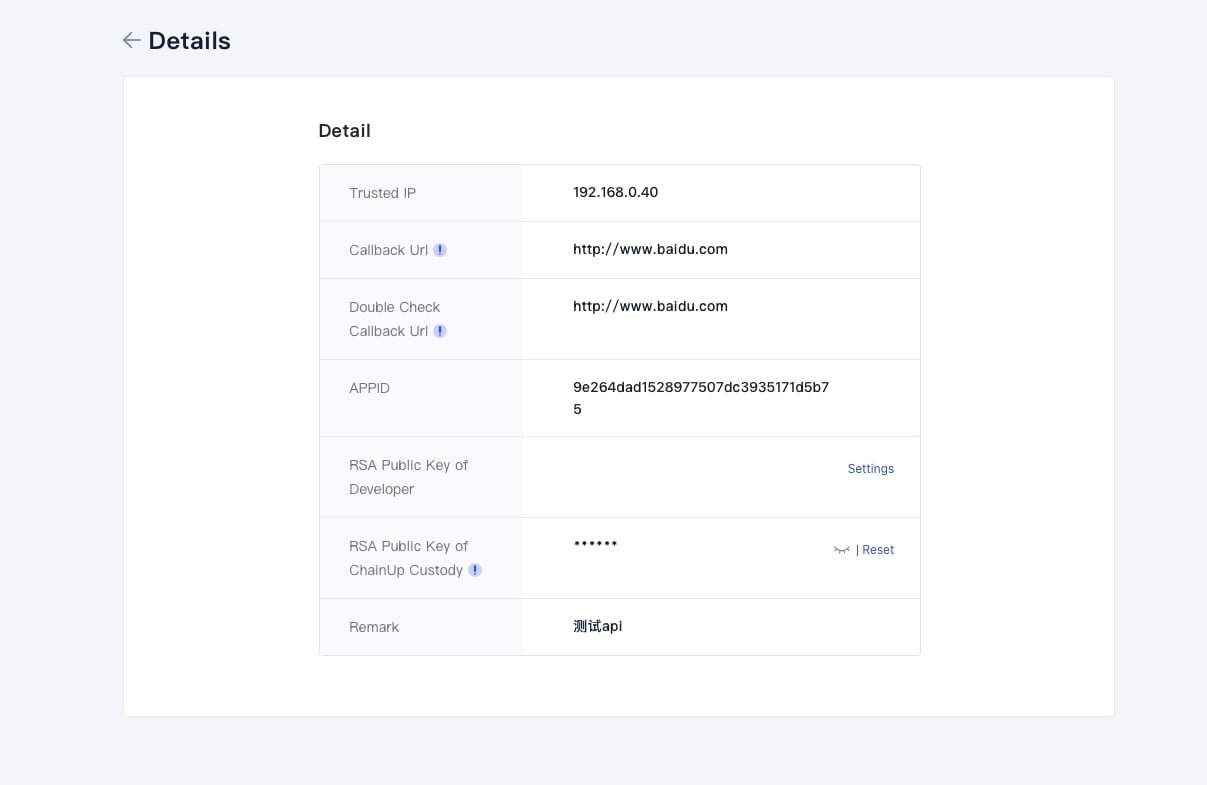
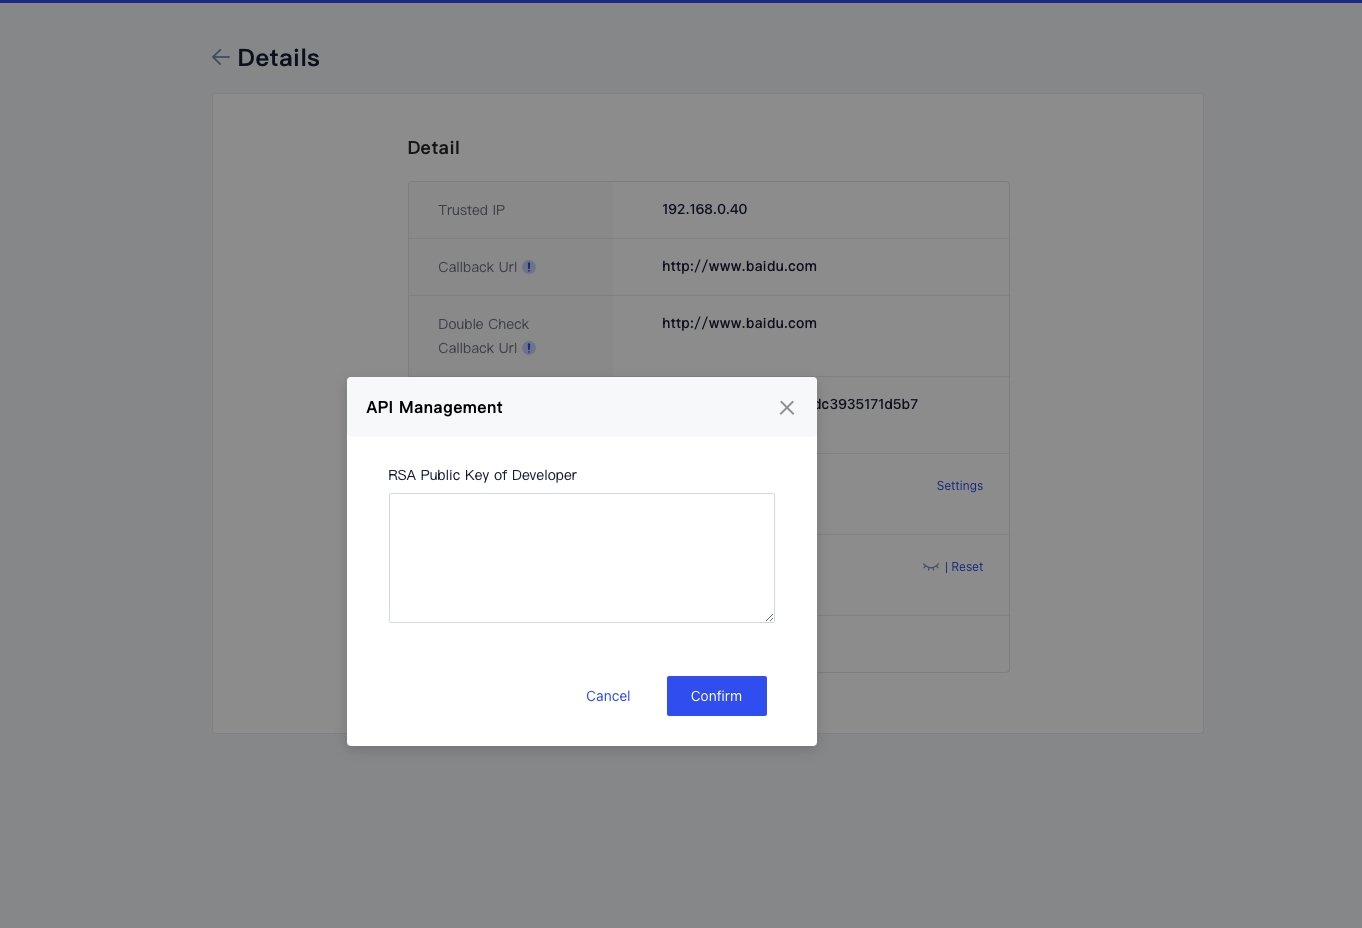
- The first pair of public and private keys: The developer shall generate a pair of public and private keys in advance when opening the asset management account. The public key (rsa_third_pub) is provided to the platform and the private key is kept by itself. The private key is the only proof for the third-party application to call the wallet service and shall not be disclosed to anyone. When the third party requests the wallet service, the private key is used to encrypt the request parameters. When the platform receives the request, the public key (rsa_third_pub) is used to decrypt the request data.
- The second pair of public and private keys: After the developer opens the asset management account, the platform will provide the wallet public key (rsa_wallet_pub) to the developer. When the third-party application receives the response data or asynchronous notification of the wallet, it needs to use the public key to decrypt.
Why is it necessary to confirm the withdrawal twice (API method)
When the wallet service receives a request from a third-party application, in confirm that the request is a legitimate request from a third-party application, it will call the interface provided by the third-party to confirm. To a certain extent, this process can avoid the influence caused by the loss of the third party’s private key, and also provides an effective barrier for the security of the wallet service.
Recommended password length:
2048
Recommended key format:PKCS#8
Account preparation
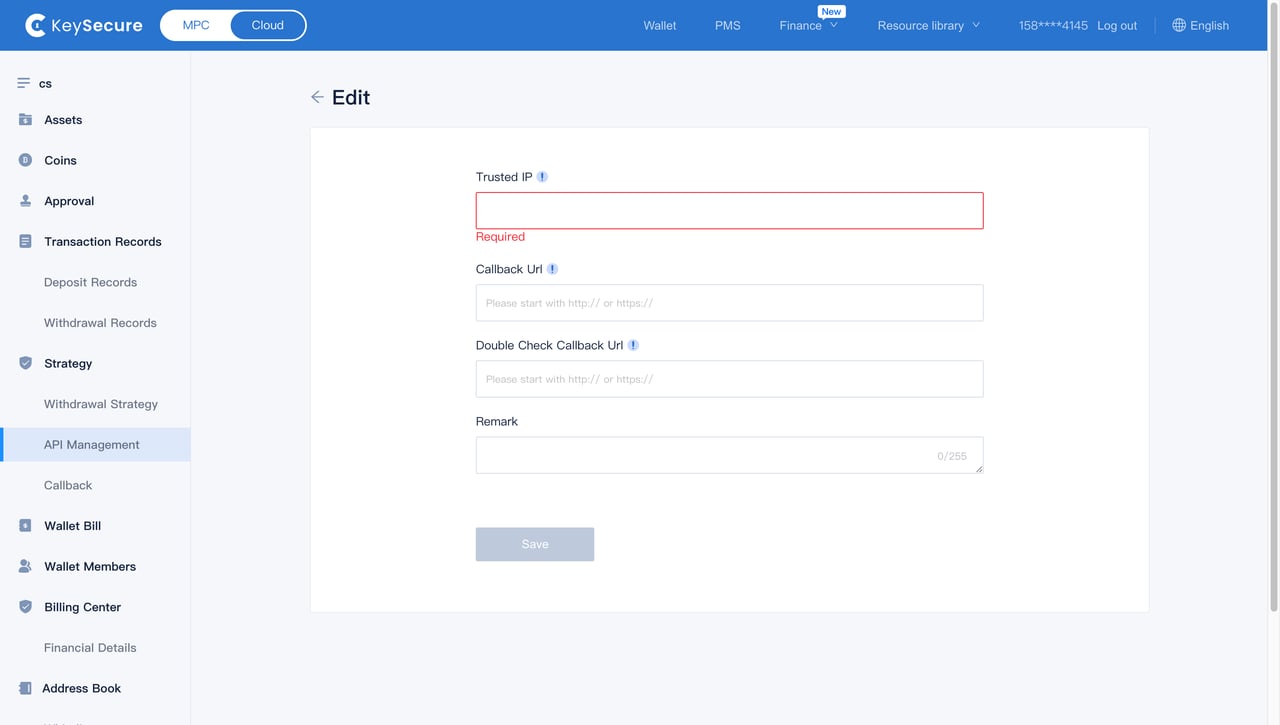
The developer prepares the following information:- Generate a pair of public and private keys.
- IP address of the third-party application server.
- Recharge and withdrawal callback notification URL.
- Withdrawal secondary confirmation URL.
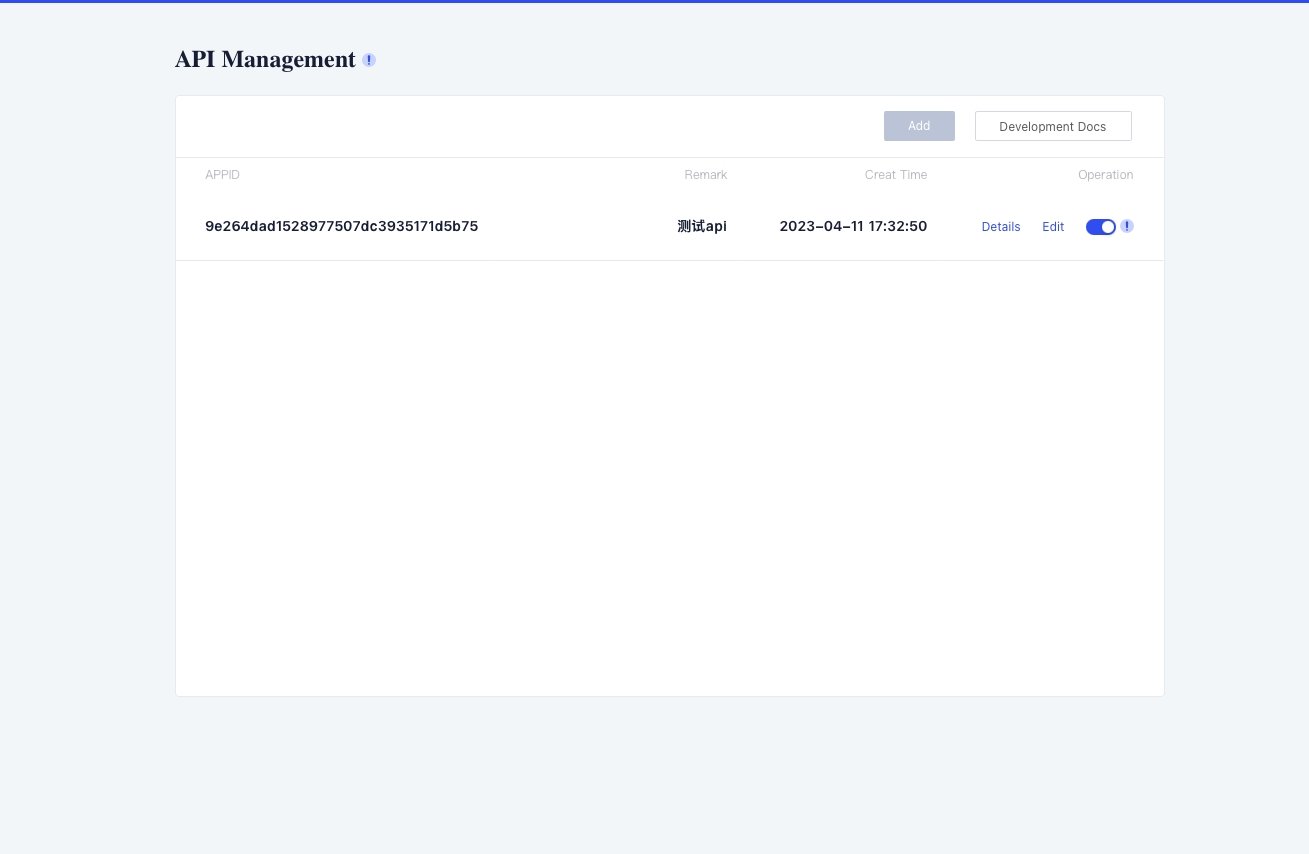
Only the wallet creator can edit the API information.
Interface Process
Documentation is the interface that the wallet service provides to third-party applications. The interface providers in the following documents are referred to as wallet services,and the interface callers are referred to as third-party applications. When the third-party application requests the wallet service, it encrypts the request parameters through the RSA algorithm and decrypts the response data after receiving the wallet service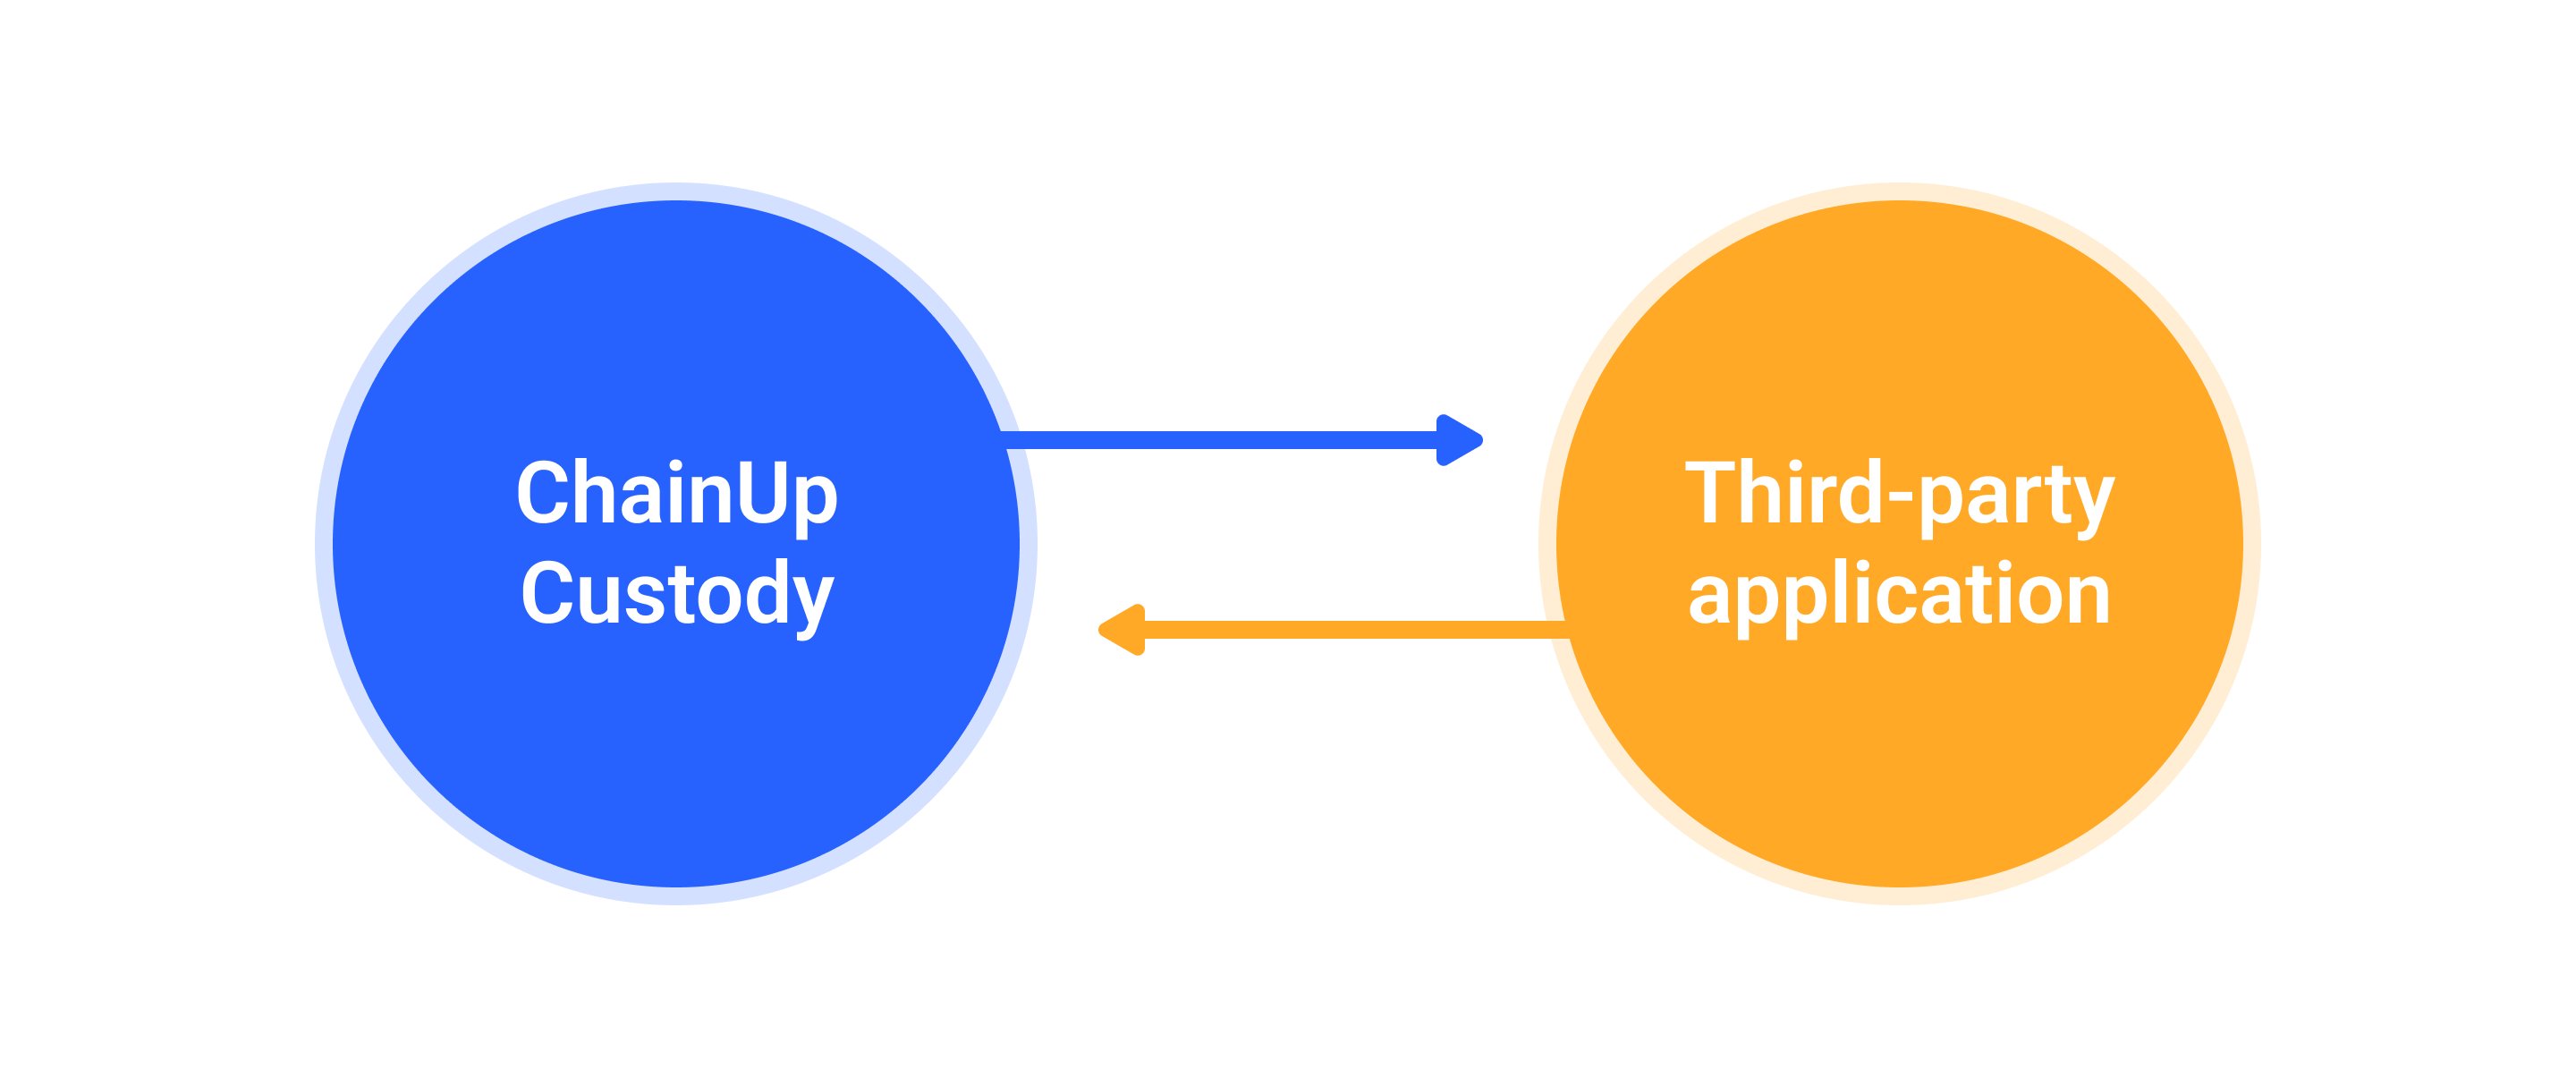
- Inbound: Allow access from the Keysecure server (IP: 54.254.7.206) to the third-party applications.
- Outbound: The third-party applications server needs to access the Keysecure server, so grant permission to access 54.251.87.91:443.